The First Chamber of the Court of Justice of the European Union (CJEU), in its judgment of 15 October 2026 (Case C-70/25, Tukowiecka), has clarified a question of great interest to consumers who fall victim to phishing: whether a bank may refuse to refund an unauthorised transaction immediately on the ground that the customer acted with gross negligence.
The answer is no. The Court holds that gross negligence attributed by the bank to the customer does not release it from the obligation of immediate refund. The bank must refund first and only afterwards, if it proves such negligence, may it claim the losses back from the customer.
The facts
The dispute stems from a fraud suffered by an account holder at a Polish bank. A third party, posing as a buyer of an item she was selling on an online auction site, sent her a link that appeared to come from that site. The link led her to a page imitating her bank’s website, where she entered her online banking credentials.
Using those details, and a confirmation code sent by SMS that he obtained from the customer by deception, the fraudster transferred PLN 3,000 (about EUR 705) to his own account. The following day, the customer reported the transaction to the bank and to the police.
The bank refused to refund the amount, arguing that the customer had breached, through gross negligence, her obligation to safeguard the payment instrument. Faced with that refusal, she sued the bank and the Polish court referred the question to the CJEU.
Specifically, the District Court of Koszalin asked the CJEU whether a bank may refuse to refund immediately the amount of an unauthorised payment transaction where it considers that the customer suffered the loss by breaching, through gross negligence, her obligation to protect the payment instrument and its credentials.
The Court’s decision
The Court of Justice addresses the question through a combined reading of Articles 73 and 74 of Directive (EU) 2015/2366 (PSD2), having regard, in accordance with its settled case-law, to their wording, their context, the objectives they pursue and their legislative history.
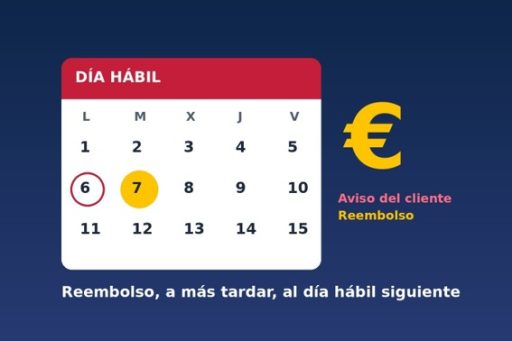
As regards the wording, the Court recalls that Article 73(1) requires the payer’s provider to refund the amount of the unauthorised transaction immediately and, in any event, no later than by the end of the following business day after noting or being notified of it. The provision admits a single exception, namely where the provider has reasonable grounds for suspecting fraud and communicates those grounds in writing to the relevant national authority. It follows that a mere suspicion of gross negligence on the part of the payer is not among the grounds permitting that refund to be withheld.
The reading of Article 74(1) is more complex, since its wording, as the Court acknowledges, does not unambiguously determine the scope of the exception it lays down. Two interpretations were possible: that gross negligence releases the provider from the immediate refund, or that it affects only the definitive nature of the refund, so that the bank must refund first and, where appropriate, seek recovery afterwards.
The systematic analysis tips the balance towards the latter. Recital 71 of the Directive refers, as an exception, only to a well-founded suspicion of fraud notified to the competent authority, and Article 72(2) places on the provider the burden of proving the user’s gross negligence. For the Court, that allocation of the burden of proof reflects the general scheme of the regime, which seeks to strengthen the payer’s protection, and confirms that the two provisions operate at different stages: Article 73 governs the immediate refund, whereas Article 74 governs the final allocation of liability at a later stage.
A teleological interpretation leads to the same result. Accepting that gross negligence dispenses with the immediate refund would deprive that obligation of its practical effect and force the payer to take the initiative of claiming before the courts, bearing the attendant inconvenience and, in particular, any legal costs. In the Court’s view, such an allocation of risk to the customer’s detriment is difficult to reconcile with the objective of ensuring a high level of consumer protection. This does not, however, prevent the provider from subsequently claiming the losses from the payer if it establishes gross negligence.
The legislative history corroborates that conclusion. Directive 2007/64 laid down no exception to the immediate refund obligation, nor did the Commission’s initial proposal. The specific exception for suspected fraud was introduced only during the legislative process, and Member States may not maintain or introduce different provisions, in view of the principle of full harmonisation enshrined in Article 107 of the Directive.
Finally, the Court dismisses the argument of the Czech and Italian Governments that this interpretation would circumvent the alternative dispute resolution procedures of Article 102. Those mechanisms cover any dispute concerning Titles III and IV of the Directive and cannot be regarded as a mandatory step for verifying the user’s compliance with the obligations under Article 69.
On those grounds, the Court rules that Articles 73(1) and 74(1) of Directive 2015/2366 must be interpreted as meaning that a payment service provider may not refuse to refund immediately to the payer the amount of an unauthorised payment transaction on the ground that the payer made it possible by acting with gross negligence in breach of his or her obligations.
Economic Criminal Law and Criminal Compliance
Specialists in economic and corporate crimes. Criminal defence in complex cases and plans for the prevention of crimes and money laundering. We act before national and European courts with total rigour. Learn morePosition under Spanish law
In Spain, PSD2 was transposed by Royal Decree-law 19/2018 on payment services. Article 45 lays down the same immediate refund obligation, the only exception being a well-founded suspicion of fraud notified in writing to the Bank of Spain. Article 44 places on the bank the burden of proving fraud or gross negligence, and Article 46 governs when the user bears the losses.
In judgment 571/2025 of 9 April, the Spanish Supreme Court had already described the bank’s liability as quasi-strict and held that the mere use of credentials does not prove the customer’s consent. Many Provincial Courts assess gross negligence restrictively, on the basis that the deception inherent in phishing generally excludes it. The CJEU judgment adds a key element: the order in which the parties must act.
Practical significance of the judgment for consumers
For consumers, the rule is now clear: the money is refunded first and fault, if any, is discussed afterwards. It is sufficient that the transaction was unauthorised and was reported without undue delay (and in any event within thirteen months of the debit).
For banks, the institution may not withhold the amount while it assesses the customer’s conduct. To recover the loss, it must claim it afterwards and prove gross negligence. Only a reasonable suspicion of fraud by the customer, notified in writing to the Bank of Spain, allows the refund to be suspended.
Avenues for redress are strengthened. Consumers may turn to their bank’s customer service department and then to the Bank of Spain or the courts. Refusing to refund on time now amounts to breaching an obligation expressly interpreted by the CJEU.
In short, the judgment places on the bank, not on the victim, the burden of taking the initiative. It is a valuable tool for all phishing, smishing and vishing claims currently rejected on grounds of gross negligence.
